Home / Platform
The platform.
A three-layer, hardware-anchored architecture. Identity lives in a physical device, policy is enforced at Core, Edge and Cloud independently, and one credential covers every system, application and door. This page is written for the security architect who wants the mechanism, not the pitch.
Architecture overview
One root, three layers, one credential.
Every existing defense shares one flaw. Identity providers, MFA apps, endpoint agents, VPNs, SSO portals and password managers are all software asking you to trust a secret. Secrets can be copied. Trustera moves trust out of software and into hardware, the way global payments did decades ago, and builds the whole architecture on that root.
Root of trust
A hardware security module in every card generates its key pair on issue. The private key never leaves the enclosure. Authentication is a signature the card produces, not a secret the system receives.
Three layers
Core holds identity and policy. Edge enforces at every device and network entry point, locally. Cloud watches the whole environment. Each works alone and together.
One credential
Workstation, applications, network, cloud, physical doors, IoT and OT, remote sessions. One card, issued in under sixty seconds, revoked from everything at once.
Hardware root of trust
The device, the key pair, the signing sequence.
The Trustera card is a credit-card-sized hardware security module with Bluetooth and NFC, a tamper-proof enclosure and PIN-protected access. On issue it generates a unique cryptographic key pair inside the device. The private key is never exported and never transmitted. It exists only to sign.
Four attack classes it removes
- Remote hacking. The key has no network exposure to attack.
- Phishing. No credential is ever typed or transmitted, so there is nothing to capture.
- Man-in-the-middle and credential theft. A relayed signature is bound to one request and one card.
- Deepfake authentication. A synthetic voice or face cannot produce a hardware signature. The attack class does not apply.
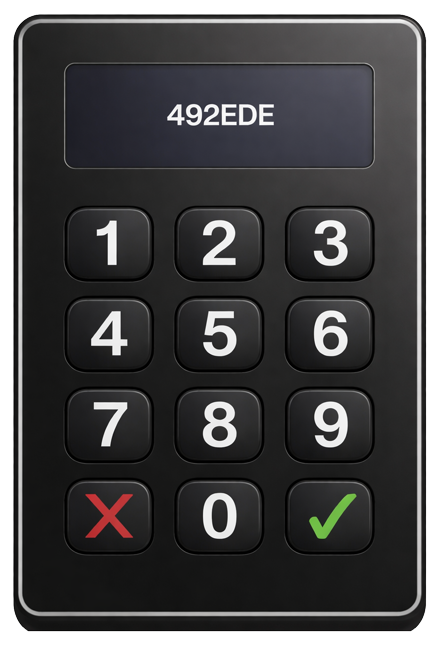
HSM · Bluetooth/NFC · tamper-proof · PIN protected · credit-card size
- 01System requests authentication from the card
- 02Card signs the request with its private key
- 03Card sends the signature. No key is sent
- 04System verifies using the registered public key
- 05Access granted, cryptographically proven, audit record hardware-signed
Zero passwords
No secrets are entered, transmitted or stored on shared systems. Nothing to phish, guess or brute-force.
Cryptographic certainty
Every authentication is mathematically verified. Only that card's private key could have produced the signature.
Hardware proof
The identity is bound to a physical object. The credential cannot be copied.
Future-proof
The same cryptographic model used by governments, militaries and financial institutions. Proven, audited, and post-quantum ready.
Tri-layer enforcement
Core · Edge · Cloud
Every layer works independently and together. There is no single point of failure: trust is enforced at the hardware level, at the network edge and in the cloud simultaneously. Compromising one does not open the others.
Trustera Core
Identity, policy & orchestration
The brain of the platform. Manages all identity definitions, access policies and cryptographic operations. Every user identity is hardware-bound and cannot be duplicated or stolen.
- Hardware-anchored identity verification: physical card plus cryptographic key pair
- Policy creation, distribution and real-time enforcement across all connected systems
- Cryptographic trust operations: sign, verify, encrypt at the hardware level
- Compliance automation: audit logs auto-generated for CMMC 2.0, NIST and SOC 2
Trustera Edge
Secure endpoint & network enforcement
The enforcement layer. Every device and network entry point is controlled here. Identity is verified at the hardware level before any access is granted, network or application.
- Real-time identity enforcement at every device and network entry point
- Local processing: low-latency decisioning without cloud dependency
- Hardware-anchored protection against spoofing, man-in-the-middle and deepfakes
- Encrypted, mutually-authenticated tunnels between every node on the network
Trustera Cloud
Visibility, intelligence & control
The visibility layer. SI-driven analytics detect anomalies across the entire environment. Administrators see everything, manage everything and respond to threats from one dashboard.
- SI-driven analytics and behavioural anomaly detection across all users and systems
- Unified dashboards: enterprise-wide visibility from one control plane
- Centralized monitoring, reporting and policy update distribution
- Native integration with SIEM, IAM, MDM and MDR platforms
Trustera Card · Unified Identity as a Service
The card is the credential, for everything.
Think of a VDI golden image, where a new employee logs into a virtual desktop and every application they need is already installed, configured and ready. Trustera does this for identity and access across every system in the organization.
When a new user receives their Trustera card they are immediately live. The card is cryptographically linked to the user's identity at the hardware level. When presented to any Trustera-enabled system it validates who the person is, what they are allowed to access, and whether that access is permitted right now, based on role, time, location and policy.
No setup. No IT ticket. No username. No password. No SSO portal. No MFA code. No separate door badge.
Workstation login
Card tap unlocks the desktop with immediate full access to authorized applications.
Network & cloud access
Hardware-verified network admission. No VPN. No separate cloud login. Zero Trust enforced.
Enterprise applications
Every SaaS and on-prem app auto-configured. No SSO prompts, no app-specific passwords.
Physical door security
The same card opens authorized doors and rooms. One credential for physical and digital access.
IoT & operational systems
Secure access to industrial, medical and OT systems using the same identity framework.
Remote & mobile sessions
Zero Trust remote access. Authenticated instantly from any device, any location.
Trustera Mod
Identity for machines.
The same cryptographic model, applied where no conventional security product operates. Trustera Mod gives IoT devices, OT equipment, SCADA and ICS controllers, medical devices and industrial systems a hardware-anchored identity of their own, so every machine-to-machine connection is signed, verified and logged.
- SCADA and ICS operator authentication at the control layer
- Anti-spoofing for operational technology networks
- Medical device and building-system identity management
- Offline and air-gap capable for isolated sites
SI Trust Engine
Continuous re-verification, not a one-time login.
The Super Intelligence (SI) Trust Engine runs in the Cloud layer and feeds Edge enforcement. It does three specific things. It does not replace the hardware root; it watches everything built on top of it.
Super Intelligence (SI) is the term Trustera uses for the behavioural analytics layer the industry has described as AI-driven. The capability is the same; the name says what it does rather than what it runs on.
Behavioural anomaly detection
Baselines every user and system across the environment and flags departures in real time: unusual hours, locations, access patterns or data volumes.
Continuous re-verification
Trust is re-evaluated at every access event against role, time, location and policy, not assumed for the length of a session.
Deepfake-resistant authentication
Because authentication is a hardware signature, a synthetic voice, face or writing style has nothing to act on. Analytics add a second check on the behaviour around the credential.
FAQ
Is the SI Trust Engine the same thing as an AI engine?
Yes. SI — Super Intelligence — is the term Trustera uses for the behavioural analytics layer commonly described as AI. The component was previously named the AI Trust Engine.
Deployment
On-premises, cloud, hybrid or air-gapped.
Trustera is infrastructure-agnostic. It integrates natively with existing enterprise systems without rip-and-replace, and most environments are live in under 30 days.
On-premises
Core and Edge inside your data center. Cloud analytics optional.
Cloud
Hosted Core with Edge enforcement at every endpoint and entry point.
Hybrid
Core on-premises, Cloud visibility across sites and remote workforces.
Air-gapped
Full enforcement with no cloud dependency, for SCIF and isolated OT environments.
Compliance automation
Hardware-signed evidence at every access event.
Audit logs are generated automatically at every access event, hardware-signed and tamper-proof. Requirements under CMMC 2.0, NIST 800-53, SOC 2, HIPAA and FedRAMP are met and documented with zero manual compliance reporting effort.
Open the compliance center- CMMC 2.0 Level 2
- NIST 800-207
- NIST 800-53
- FedRAMP-ready
- SOC 2 Type II
- HIPAA
- PCI-DSS
Next step
Walk through the architecture with an engineer.
A technical demo covers key issuance, policy enforcement at each layer, and how Trustera lands in your existing stack.